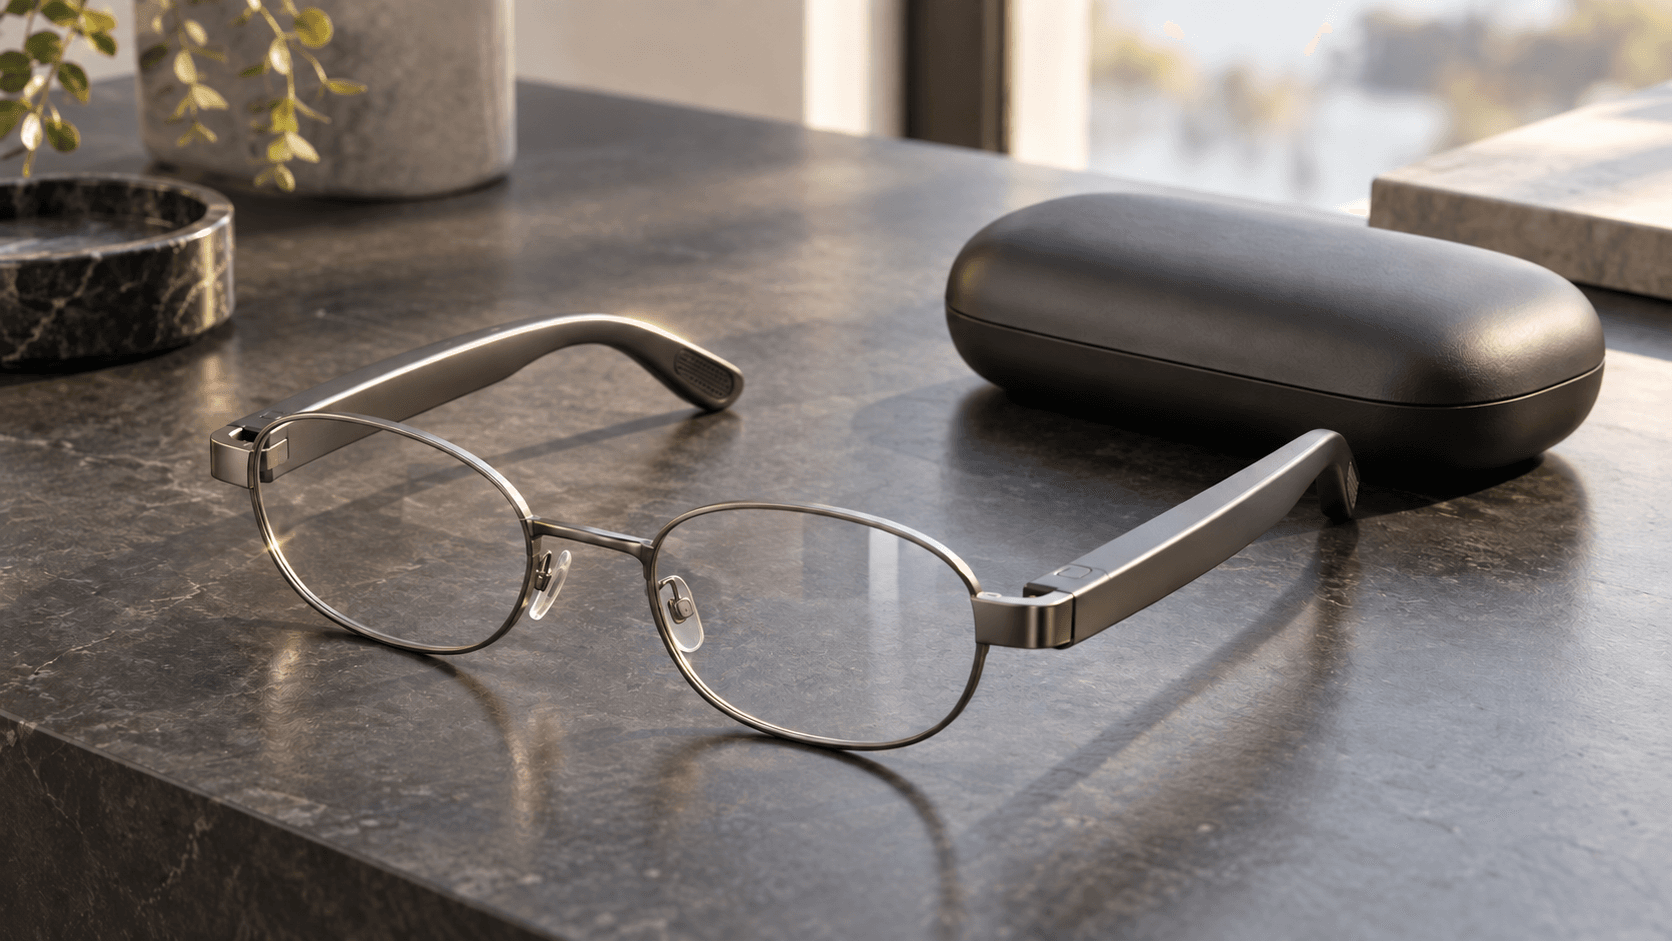
Meta's most interesting new glasses feature is a missing component. Ray-Ban Meta Audio removes the camera from wearable AI, making a straightforward promise about what the device cannot see. That is a useful product decision. It is not the same thing as settling who can hear, remember or act on the information that passes through an assistant.
Announced at Connect on September 23, the glasses start at $349. Meta says preorders are open and shipping begins October 13. The company lists a 43-gram weight and up to twelve hours on a charge, with calls, music, podcasts and hands-free AI among the uses. Those are manufacturer specifications, not results from our own battery or comfort tests. TechCrunch also reported the camera-free announcement.
The interesting question is whether a narrower device can make a stronger offer. Some people want help that stays out of their hands without turning every interaction into an opportunity for video capture. Serving that preference does not require proving that cameras are always bad. It requires acknowledging that capability is only valuable when someone actually wants the consequences that come with it.
Meta's July explanation of its camera-equipped glasses provides the relevant backdrop. The company described a capture light that signals gallery photos and video, along with safeguards intended to disable the camera when obstruction or tampering is detected. It also said gallery media stays on the glasses until the wearer chooses to import it. Those details concern the camera models, not the new audio-only pair.
A capture indicator and an absent camera solve different problems. The indicator communicates an activity and depends on people noticing and interpreting it. Removing the sensor prevents that device from performing the activity in the first place. This is why a hardware constraint can be easier to explain than another setting. It reduces the promise a product has to ask everyone nearby to believe.
Still, audio is not an empty category. An assistant asked to handle a conversation, a reminder or a work request may encounter sensitive information without receiving a single image. The practical evaluation should therefore separate four questions: what is collected, where it is processed, what persists afterward, and what actions the system can take. Calling the whole bundle private skips the work.
The Confidential Computing Consortium describes one important part of that work: protecting data while it is being used, inside a hardware-based, attested trusted execution environment. Conventional infrastructure permissions can give a privileged operator access to applications and their memory. Confidential computing aims to isolate the workload from that operator, rather than relying exclusively on rules telling the operator not to look.
For an agent, the protected material can include more than a conversation. The consortium's analysis discusses identity, authorization capabilities and the integrity of the agent itself. Protecting a secret is useful; protecting the authority associated with it is useful too. This is infrastructure security, however, not a conclusion that the agent will interpret every instruction correctly or make a sensible purchase.
The word attested deserves translation. It means the client can ask for evidence about the environment that will receive its data. The consortium's explanation describes measurements signed through a hardware root of trust and evaluated against reference values and a security policy. The system is supposed to supply something more concrete than a provider's assurance that the server is configured properly.
The distinction between evidence and judgment remains important. A measurement can identify a firmware version; someone still decides whether that version is acceptable. Trust also remains in the hardware vendor and, where used, the party verifying the evidence. Attestation makes parts of the relationship testable. It does not remove every dependency or certify that the words produced by a model are true.
Meta's September 23 engineering post extends Private Processing to glasses and describes confidential virtual machines, checks before data is sent, and encrypted storage for features that need persistent memory. The company says user-provided keys protect that stored information. Its design aims to keep the infrastructure operator outside the protected processing environment. These are Meta's architectural claims, not an independent finding that every intended protection works.
There is a consequential transparency qualification in the same post. Meta says deployed software measurements are recorded in a publicly witnessed ledger, but the corresponding binaries are available to security-program researchers under agreement. A record showing which software ran is not itself a complete explanation of that software's behavior. Access conditions matter when judging how broadly outsiders can test a privacy claim.
That is a more substantive conversation than asking whether cloud AI is inherently trustworthy or inherently hopeless. The buyer should want to know which feature enters the protected environment, what evidence the client checks, and what happens when a check fails. A strong mechanism applied to only part of a workflow cannot automatically supply guarantees for every other part.
Persistent memory also changes the engineering problem. Meta's original April 2025 account of WhatsApp Private Processing described a stateless service: messages would not remain durably accessible to the service after a session. That approach suits a bounded task such as producing a summary and returning it. A service designed to recall information later has a different job to perform.
The older threat model is refreshingly explicit that isolation is not magic. It discusses malicious inputs, prompt injection, software exploitation and the tension between debugging and confidentiality. The lesson for the new wearable design is to ask how those risks are handled in the actual workload. A protective boundary does not excuse careless code running inside it, and sensitive diagnostic output can become another way data escapes.
Apple's June 2024 Private Cloud Compute design offers a useful historical comparison, not a claim about a new Apple wearable. It described stateless handling of requests, limits on privileged runtime access and a restricted approach to operational logs and metrics. The ambition was to prevent maintenance access from becoming a convenient exception to the privacy promise.
Apple also committed to making production software inspectable and tying client connections to verifiable software measurements. That establishes a useful evaluation standard: can researchers inspect the relevant implementation, and can clients connect the implementation they were told about to the one actually serving them? Comparing those mechanisms is more informative than comparing adjectives in launch presentations. It is not enough to declare either company's entire system the winner.
The maintenance tradeoff deserves attention from anyone building an AI product. Suppose a personal assistant fails on a sensitive request. An engineer might ordinarily want the input, output and surrounding state to reproduce the bug. A genuinely restrictive privacy design can make that unavailable. The correct response is to design diagnostics around the boundary, not add an emergency exception that quietly turns the promise off.
Action permissions form another boundary entirely. Meta's September 8 Muse announcement described user-selected service access, confirmation before sensitive actions, an audit trail and a separate Sentinel that checks activity before it reaches the internet. That was part of the existing agent launch. The new relevance is the prospect of reaching that agent from glasses, where speaking a request can feel less deliberate than completing a form.
A useful hypothetical is asking an assistant to deal with an appointment while walking between meetings. Finding available times, drafting a message, sending it and paying a fee are different permissions. The user's casual phrasing should not collapse them into one decision. Encrypting the request protects its handling; it does not decide which of those steps the user intended to authorize.
Meta's earlier Muse announcement also distinguished its Secure VM from a Confidential VM planned for later in the year. That distinction should remain visible when evaluating the glasses roadmap. Similar names do not establish identical guarantees. Nor does an announcement of a future confidential mode prove that every current interaction already uses it. Product availability and architecture need to be checked together.
The September 23 glasses software roadmap reinforces that caution. Meta presents bringing Muse and Private Processing to glasses as work underway, alongside forthcoming capabilities. It describes an assistant that can continue tasks in the background and notify the wearer when finished. The document is a roadmap, not evidence that every announced feature is enabled for every device, account and region today.
That mixed lineup also creates a basic compatibility trap. Features involving what the wearer sees cannot be assumed to work through a camera-free frame. Buyers need a feature-by-device account of what remains available through audio and what requires visual input. A capability demonstrated somewhere in the glasses family is not automatically a capability of the specific pair someone is ordering.
For a workplace trial, our recommendation is to start with a defined task and an explicit data boundary. Use non-sensitive examples to establish whether the interaction is actually better than the existing phone workflow. Then check what records can be reviewed or removed, which connected services receive access, and where a consequential action requires confirmation. These are acceptance questions, not claims that we have tested the finished product.
The commercial opportunity is credible precisely because it can be narrow. Calls and an accessible assistant do not need to carry the burden of proving that everyone wants a camera on their face. But a more acceptable shape is only the opening move. The daily experience still has to earn its place through usefulness, predictable behavior and controls people can understand without studying a security paper.
Meta has made one boundary unusually easy to understand: this pair has no camera. The next test is whether the less visible boundaries become just as clear. What leaves the device? What remains in memory? What can the assistant do without asking again? Answer those concretely and the product has a stronger case. Leave them buried under a general privacy slogan and the missing camera will have done only part of the job.
LaunchPad positionEvaluate capture, processing, retention and action permissions separately. A missing camera and a cloud security design make different promises.
This report draws on the linked primary sources and reputable reporting. Company statements are treated as claims until independently demonstrated.